*Inhalt gelöscht*
Zuletzt bearbeitet von einem Moderator:
Follow along with the video below to see how to install our site as a web app on your home screen.
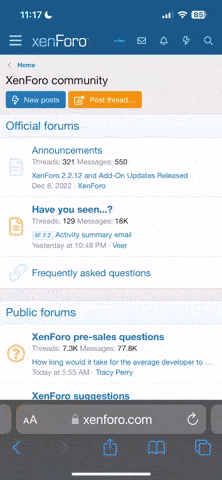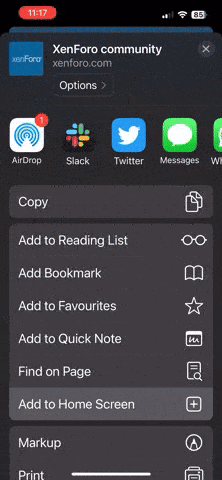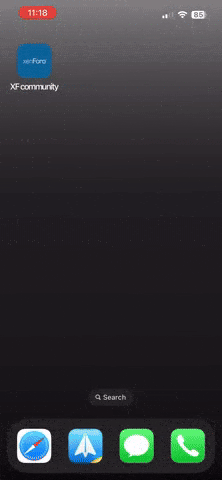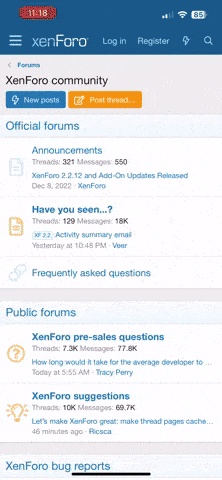
Anmerkung: this_feature_currently_requires_accessing_site_using_safari

Spannend, das kann man auf jeden Fall weiterverfolgen.und vielleicht bald nfSensei.

Vielleicht doch nicht.Ich werd mir dann auch weitere Posts zur Plus hier sparen.

For clarity the Home and Lab Evaluation subs are still valid.
Absolut. Z.B: VPP fast path, also Vector Packet Processing in der Firewall, es klingt fast zu schön. Mal sehen, was aus Gedanken und Träumen einer fachkundigen Person und KI in der Praxis tatsächlich an Firewall rauskommt.Spannend

Gibts alles schon: https://www.netgate.com/tnsrAbsolut. Z.B: VPP fast path, also Vector Packet Processing in der Firewall, es klingt fast zu schön. Mal sehen, was aus Gedanken und Träumen einer fachkundigen Person und KI in der Praxis tatsächlich an Firewall rauskommt.
Nun final.Kann man so nicht direkt sagen, finde ich.
 www.netgate.com
Today we are rolling out the wireless device MVC/API rework and a
final push for better source NAT replacement over outbound NAT.
Strongswan was updated to 6.1.0 and the GUI now offers a small
recommended set of post-quantum key exchanges.
You may also find the GUI tweaks for advanced option marker and
a dialog search field helpful.
There is a lot more going on as you can see from this changelog,
but more on this and future plans later!

This update finally brings interface settings to MVC/API! It also brings
a number of fixes and improvements from FreeBSD stable/15 including a fix
for previous Hyper-V boot issues and hopefully also fixes ice driver DDP
issues with newer firmware versions.
For the interface settings MVC/API there a few things to keep in mind:
o You can find them on the assignments page integrated into the existing grid.
o Commonly required DHCP advanced options not in basic mode have been made available.
o Advanced/file based modes for DHCP are gone and will reset on save.
o Saving settings queues them for reconfiguration and storage.
o A reboot without apply will discard the previously saved changes.
o Apply works similar to the old interfaces.php page but uses a rewritten backend sequence.
o The old interfaces.php page is still available retaining the old style settings.
o The old interfaces.php page will likely move to a plugin for 27.1.
We are looking for your feedback on this historic milestone!

 Premium-Membership 2027 Supporter
 Premium-Membership 2026 Supporter
 Premium-Membership 2025 Supporter
 Premium-Membership 2024 Supporter
This release is mainly for the brave Hyper-V users who fought kernel panics
since 26.7, which got fixed in 26.7.6 only to cause segmentation faults for
others. Thanks all for testing and correcting the problem in FreeBSD!
The other reason are fixes in the new interfaces settings API so that it
more closely matches the behaviour of the legacy page.
Both the iPerf and the FRR plugin have been reworked substantially. In case
of FRR please read the migration notes linked below before updating.
Here are the full patch notes:
o interfaces: add missing validation for "configurable" and "spoofmac" in new settings API
o interfaces: only store "dhcp6_norequest_dns" in DHCPv6 mode in new settings API
o interfaces: only store "track6-interface" in ID association / Track interface modes in new settings API
o interfaces: do not render "none" to configuration in new settings API
o interfaces: move promiscuous mode to advanced in new settings API
o interfaces: fix index into $todo for proper flag check during apply in new settings API
o interfaces: provide better option group labels to DeviceField
o interfaces: add proper local/remote IP support to PPPoE IPCP
o interfaces: move legacy apply cache to /var/lib/php/tmp
o firewall: destination NAT: fix typo in parseRdrRules() causing faulty rules not being disabled
o firewall: aliases: validate that port aliases always have content
o firewall: revert a clone rule change so that cloned rules to appear adjacent to the original rule again
o mvc: UidField: add isolated updateValue() for installer user
o ui: bootgrid: sync columnselect-input state with (un)setColumns
o ui: sync expanded state for selected submenus
o ui: close mobile menu when a menu entry opens another tab of the current page (contributed by Greelan)
o plugins: os-ddclient 1.33[1]
o plugins: os-frr 2.0[2]
o plugins: os-iperf 2.0[3]
o src: pf: send syncookies from the receiving thread
o src: hyperv: fix two regressions in previous upstream patch
o src: pcib: only apply ARI translation to the own secondary bus of a bridge
o src: ktls CBC decrypt: avoid creating zero length iovec entries
o src: route/fib_algo: respect immediate_sync in fd_ref_nhop
o src: route/fib_algo: fix FIB_ALGO without ROUTE_MPATH option
o src: sysctl: retire SYSCTL_NODE_CHILDREN()
Stay safe,
Your OPNsense team
--
[1] https://github.com/opnsense/plugins/blob/stable/26.7/dns/ddclient/pkg-descr
[2] https://github.com/opnsense/plugins/blob/stable/26.7/net/frr/pkg-descr
[3] https://github.com/opnsense/plugins/blob/stable/26.7/benchmarks/iperf/pkg-descr
. Ist die Regel deaktivert funktioniert VoIP nicht mehr 🤬